From first call to a signed, evidence-backed report
Seven steps, one person, and Ward, the assessment platform behind every SaberGuard risk analysis. You never install anything and you never log in to a portal.
Scoping call
You and Jonathan · 30 min
What triggered the search, how many people and locations, which platform you run (Microsoft 365, Google Workspace, or both), and which EHR. You leave with a fixed fee and a start date.
Fixed-fee proposalRead-only access
Your administrator · 15 min
Your admin grants Ward a read-only, configuration-only connection to your tenant. It is one isolated credential no other client shares, and your admin can revoke it at any time.
Scoped collection setupShort attestation
You · about an hour
A plain-language questionnaire about the things software can't see: physical safeguards, business associate agreements, how staff use the EHR, what happens when someone leaves.
Attestation on fileWard collects and evaluates
Automated · scheduled
Ward pulls your security configuration, normalizes it into plain facts, and checks each one against a hand-written rules corpus for practices like yours. A rule, not an AI, decides whether a control is met and how serious a gap is.
Candidate findings, each tied to evidenceReview and sign
Jonathan, CISM
Every finding is read by a person. What doesn't hold up is edited or rejected. What does is written in plain language, cited, rated, and signed. His name is on the report.
Signed risk analysis + Massachusetts WISPFindings review and remediation
You and Jonathan
A working session on what to fix first, what can wait, and what to tell your insurer. Remediation is quoted per project and done by SaberGuard, or handed to your IT provider.
Prioritized roadmap, remediation quotesKeep watching (optional)
Ward + Jonathan · on a schedule
The same read-only access stays in place. Ward re-collects on a schedule, a change that trips a rule becomes a candidate finding, and Jonathan reviews it before you hear about it. Drift becomes a finding, not a surprise.
Report kept current, scoped on requestWard reads configuration, not patients
Ward reads your security configuration: who has MFA, who holds admin rights, how sharing is set, whether devices are managed. It never reads email, files, calendars, or patient records. Every finding points at the configuration that produced it and the moment it was observed.
What Ward reads
- MFA registration state
- Conditional access and security defaults
- Admin role assignments
- Stale accounts
- External sharing settings
- Device compliance
- Licensing
What Ward never reads
- Files
- Calendars
- Chat
- Patient records
- Anything a patient wrote
The access is read-only. Your administrator grants it and can revoke it at any time.
The evidence chain
- 01
Raw configuration
hashed, archived immutably
- 02
Fact
mfa_registered = 0 of 3
- 03
Rule
a rule decides, not an AI
- 04
Finding
cited, rated, evidence attached
- 05
Reviewed
signed by a CISM
Every finding in your report points at the configuration that produced it, the time it was observed, and the rule that fired. If a finding is ever questioned, the evidence is there.
One credential per client
Each practice gets its own isolated credential. Revoking yours affects only you.
Immutable evidence
Collected configuration is hashed and stored under an immutability policy. It cannot be edited after the fact.
No patient data, ever
Ward does not request, receive, or store patient records or any content a patient wrote. Hosted in Microsoft Azure.
SaberGuard assesses and advises; it does not warrant compliance.
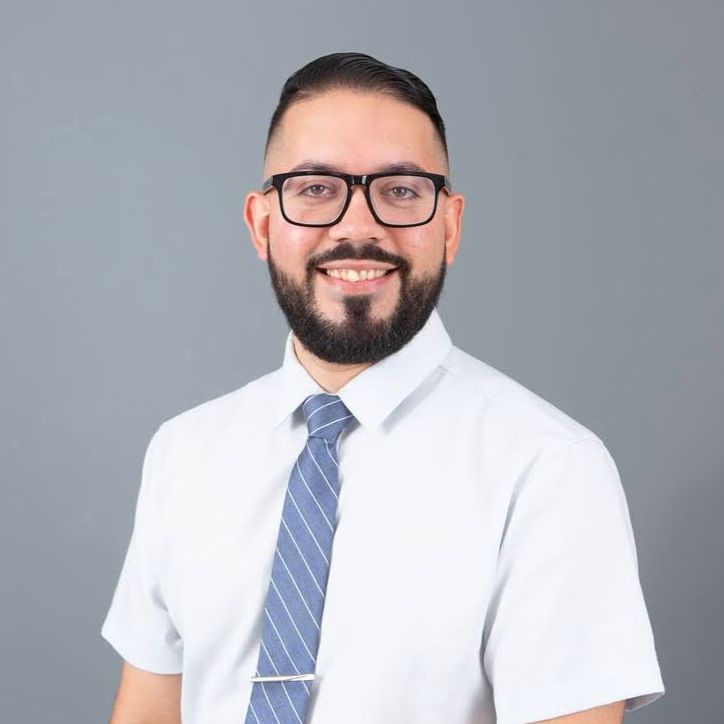
“You are not buying a binder. You are buying the ability to answer, on the day someone asks, exactly what you did to protect patient data — and to show your work.”
SaberGuard is deliberately small. You work directly with the person doing the assessment — there is no junior analyst running a template and no account manager between you and the findings.
Read the full background